How to authorize and remember central on user request?

Hello,

I am developing a peripheral device, on which the firmware shall prevent unauthorized access to some custom characteristics. Once a central device is authorized, the peripheral device shall allow the access to these characteristics. The authorization shall happen only after an explicit user action (the user has to press a button on the peripheral to allow this). Once a central device is authorized, the peripheral device shall grant full access to the characteristics in the following power cycles automatically, without any user action.

My question is, how can I achieve this in the most straightforward way? Shall I add some protection to the characteristics through bonding and allow the bonding only after the user requested it? Or would it be more intuitive to use whitelisting (after bonding) and allow the bonding onyl after user request? I am happy to hear you suggestions, with some detailed description.

Thanks.

Adam

Target hardware is nRF52810, with softdevice s112, 7.3.0.

Parents
  • Hello Adam,

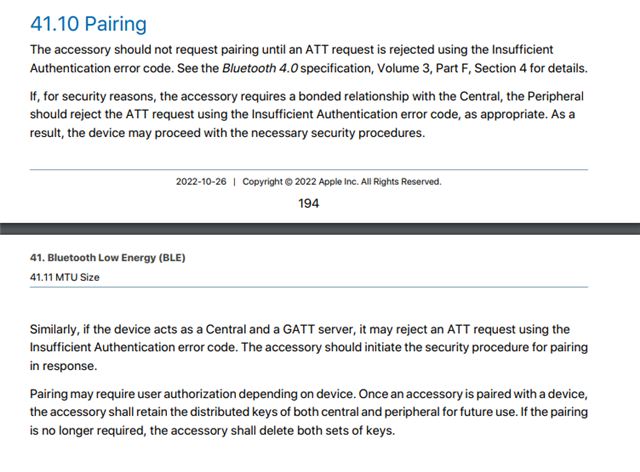
    Some centrals, such as iOS, will automatically prompt the user to pair if they discover a characteristic that requires authentication. This is actually the only way to bond with iOS as it does not expose any APIs for bonding.

    From their Accessory Design Guidelines Document (https://developer.apple.com/accessories/Accessory-Design-Guidelines.pdf)

    So, it would be confusing to the user if they are asked to pair by the phone to then have the pairing rejected by the nRF device.

    Could an approach be to use just works for all connections and handle the authentication at the application layer? The application can ignore writes, etc from the characteristics before the authentication has taken place.

    Best regards,

    Vidar

Reply
  • Hello Adam,

    Some centrals, such as iOS, will automatically prompt the user to pair if they discover a characteristic that requires authentication. This is actually the only way to bond with iOS as it does not expose any APIs for bonding.

    From their Accessory Design Guidelines Document (https://developer.apple.com/accessories/Accessory-Design-Guidelines.pdf)

    So, it would be confusing to the user if they are asked to pair by the phone to then have the pairing rejected by the nRF device.

    Could an approach be to use just works for all connections and handle the authentication at the application layer? The application can ignore writes, etc from the characteristics before the authentication has taken place.

    Best regards,

    Vidar

Children
Related