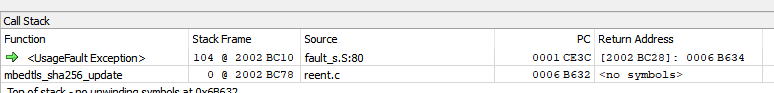
Hi Nordic Semi
As you can see in my previous ticket RSA example fails on psa_sign_hash returning -133 - Nordic Q&A - Nordic DevZone - Nordic DevZone (nordicsemi.com) getting support for RSA OAEP(SHA1) public key encryption (3072 bit keys) required me to use the mbed_tsl library and set CONFIG_NORDIC_SECURITY_BACKEND=y.
Now, for the same project I want to use ECDSA signatures. The ECDSA sample in the SDK "v2.1.1\nrf\samples\crypto\ecdsa" works just fine as long as you do not set CONFIG_NORDIC_SECURITY_BACKEND=y, then it fails indicating -135 i.e. invalid argument.
Can you please assist me in a configuration that supports both ciphers.
- SDK 2.1.1
- nRF5340
Regards Tonny