ECDSA not working with CONFIG_NORDIC_SECURITY_BACKEND and RSA not working without

Hi Nordic Semi

As you can see in my previous ticket RSA example fails on psa_sign_hash returning -133 - Nordic Q&A - Nordic DevZone - Nordic DevZone (nordicsemi.com) getting support for RSA OAEP(SHA1) public key encryption (3072 bit keys) required me to use the mbed_tsl library and set CONFIG_NORDIC_SECURITY_BACKEND=y.

Now, for the same project I want to use ECDSA signatures. The ECDSA sample in the SDK "v2.1.1\nrf\samples\crypto\ecdsa" works just fine as long as you do not set CONFIG_NORDIC_SECURITY_BACKEND=y, then it fails indicating -135 i.e. invalid argument.

Can you please assist me in a configuration that supports both ciphers.

  • SDK 2.1.1
  • nRF5340

Regards Tonny

Parents Reply Children
  • Hi Hieu

    Thanks for your reply. I have now tested my client code towards the mbed_tsl API.
     

    The mbed_tsl API also gave me a hard time.

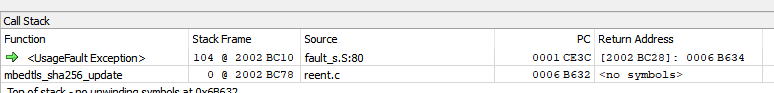
    During ECDSA signature a user-fault occurred during a sha256 operation in the function _reclaim_reent in reent.c:

      
    reent.c is part of newlibc. The name of the function suggests some reentrant operation and the comments in the file describes reclaiming memory.

    I thus tried increasing both stack and heap, but message signing still failed.

    What worked was to set 

    CONFIG_MBEDTLS_ECDSA_DETERMINISTIC=n

    I.e. use a "high quality" (most likely HW) random generator in stead of an algorithmic.

    This solved the problem when signing.
  • Hi Tonny,

    It's great that you figured it out! Thank you for sharing your experience.

Related